Blog
Go backYour Recovery Email Is a Spare Key. Treat It Like One.
Zero-Bullshit Guides · November 2nd, 2026
Somewhere in your account settings is an address you typed in years ago and haven't thought about since. It can reset your password. Whoever controls it can walk into your inbox without knowing a single thing about you.
That's what a recovery email is. Providers present it as a convenience, a way back in if you forget something. It's more useful to think of it as a spare key under the doormat. Handy if you're locked out, and exactly as handy for anyone else who knows where to look.
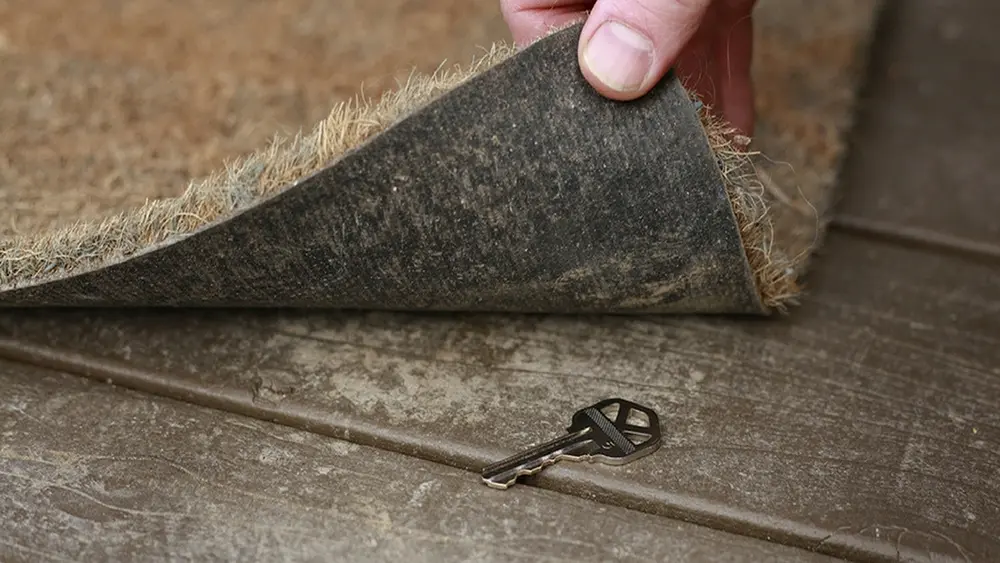 Handy if you're locked out. Exactly as handy for anyone else who knows where to look.
TL;DR
- A recovery address can reset your main password, so it needs the same protection as the account it protects. Usually it has less.
- Log into every recovery address you've ever set, today. Dead ones lock you out. Lapsed domains let other people in.
- Don't let two accounts recover each other with nothing else in the loop. Lose both at once and both are gone.
- Security questions are the weakest recovery method there is. If a service insists on them, answer with random strings and keep those in your password manager.
- A recovery phone number has the same SIM-swap problem as SMS codes. Fine as one option, dangerous as the only one.
- Recovery codes on paper and a trusted recovery contact are the two things that break every bad loop.
What a Recovery Address Can Do
Click "forgot password" on almost any service and a link arrives at your recovery address. Click the link, choose a new password, you're in. No old password needed, no second factor in most flows, no questions asked.
So the recovery address isn't a backup. It's an alternative credential, as powerful as the password itself and in one way more so: it's also where the provider sends the alert saying somebody just changed your password. An attacker who owns your recovery address resets your login and reads the warning about it, in that order.
Which means the recovery mailbox needs its own second factor, its own strong password and everything else in the 2FA article. In practice it's usually the account people secured least, because they stopped using it for anything except this.
The same logic applies one level down. Whatever recovers your recovery address can reach everything that address recovers. Follow the chain far enough and most people's entire digital life ends in a single old mailbox they haven't opened since a previous job.
The Address You Forgot You Had
The common failure is an address that no longer exists or that you can't get into. The ISP mailbox from a provider you left. The university address that was closed a year after graduation. The work account at a company you don't work for. Google now deletes personal accounts that have been inactive for two years, so a Gmail address you set as recovery in 2019 and never touched again may simply be gone.
A dead recovery address is a lockout waiting to happen. You find out when you need it.
The worse case is an address somebody else can take over, and the clearest route to that is an expired domain. If your recovery address lives on a domain, yours or an old employer's, and that domain lapses, anyone can register it, set up a mail server and start receiving everything sent there. Including password reset links.
This isn't theoretical. In 2018 a security researcher re-registered six expired domains, some of them previously owned by Australian law firms, and pointed the mail at a catch-all. Over three months more than 25,000 messages arrived: court transcripts, bank statements, client correspondence. He showed he could have reset passwords on the firms' Office 365 and G Suite accounts from the mail alone.
In 2025 the Python package index started checking every user's email domain against a registry status service, daily, and quietly unverifying addresses whose domain had lapsed, because attackers were registering expired domains and requesting password resets for the accounts attached to them. More than 1,800 addresses were unverified in the first few months. If a software repository has to defend itself against your old domain expiring, your bank's recovery flow isn't going to do it for you.
If you own a domain and use it for anything that matters, the renewal is a security control. Put it on auto-renew with a payment method that won't expire before the domain does.
The Circular Trap
Here's the one that catches careful people.
You have two email accounts. Sensibly, you've set each as the recovery address for the other. Nobody can take over one without the other, which feels like redundancy.
Now your phone goes in the river. New phone, new setup. You need to log in to account A. You've forgotten the password, which is fine, that's what recovery is for. The reset link goes to account B. You're not logged into B either. B's reset link goes to A.
Both accounts are perfectly healthy and you will never see the inside of either of them again.
The same trap appears in other shapes. A password manager whose own account recovery runs through an email address stored only inside that password manager. An email account whose only recovery route is a phone number tied to a SIM that lives in the phone you've just lost. A bank that sends reset links to the inbox you're currently locked out of.
The test is simple. Write down your important accounts and draw an arrow from each one to whatever recovers it. If you can trace a loop that never leaves the diagram, that loop is a trap. Somewhere in it there has to be an exit that doesn't depend on being logged into anything: recovery codes on a piece of paper, a hardware key in a drawer, a human being who can vouch for you.
Security Questions
Google published research on these in 2015 and the numbers are worth remembering. With a single guess of "pizza," an attacker had almost a one-in-five chance of answering an English speaker's favorite food. Ten guesses gave a one-in-five chance at a Spanish speaker's father's middle name. Meanwhile 40 percent of English-speaking users couldn't remember their own answers, and the 37 percent who'd given deliberately false answers to make them harder to guess had made them harder to remember instead.
Google's conclusion was that secret questions are "neither secure nor reliable enough to be used as a standalone account recovery mechanism," which is a polite way of saying don't.
Most serious services have dropped them. Some banks and government portals haven't. Where you're forced to use one, treat the question as a prompt for a second password: generate a random string, store it in your password manager under that account and never answer truthfully. Your mother's maiden name is on a genealogy site. Your first school is on Facebook. A random string is on nothing.
The Recovery Phone
A recovery phone number works the way SMS two-factor works and fails the way SMS two-factor fails. We went through SIM swapping in the 2FA article, and the short version is that a phone number is an identifier a carrier employee can reassign, and regulators have written rules because that keeps happening.
Keep a recovery number on file if the provider wants one. Don't let it be the only route in, and update it the day you change numbers. A recycled number is somebody else's phone now, and some providers will happily send your reset code to it.
Recovery Contacts
The newest option is also the oldest idea: a person who can vouch for you.
Apple has offered an Account Recovery Contact since 2021. Google added Recovery Contacts in October 2025. In both cases you nominate someone you trust, and when you're locked out the provider gives you a code to read to them, which they confirm from their own account. They never get access to anything of yours. They just confirm you're you.
This is the cleanest exit from the circular trap, because a human being isn't inside your diagram. Choose someone who would notice if a stranger rang claiming to be you, and tell them they've been chosen, so the request doesn't arrive out of nowhere.
The Fifteen-Minute Version
- List the accounts that matter: your email, your password manager, your phone's cloud account, your bank.
- For each one, open the security settings and write down what recovers it. Address, phone number, questions, codes.
- Log into every recovery address on that list, now. If you can't, fix or replace it before you do anything else.
- Look for loops. Break each one with recovery codes on paper or a hardware key.
- Replace every security question answer with a random string in your password manager.
- Confirm the recovery phone is a number you still hold.
- Add a recovery contact wherever it's offered.
- If you're changing email providers, update your recovery addresses everywhere before you close the old mailbox. The switching guide has the full checklist.
Where [@fuck.it] Lands
Your fuck.it account recovers through the external email address you gave us when you signed up. Forget your password and the reset link goes there. We don't use security questions and we don't collect phone numbers, so that address is the one spare key to your account, and it deserves the same care as the account itself.
Two things follow from that. Keep the address current in your account settings when you move mailboxes, because a reset link sent to a dead address helps nobody. And make sure that address isn't one that, in turn, recovers through fuck.it, or you've built the loop described above with us in it.
One password covers both your fuck.it account and your mailbox, so a reset through that external address resets everything. If the address is gone and you're locked out, the fallback is support, and support is slower than a link.
Sources & further reading: Google Security Blog: Some tough questions for security questions (2015) · Google: Recovery Contacts · PyPI: Preventing domain resurrection attacks · WeLiveSecurity: Abandoning a domain name can come back to bite you · Apple: Set up an account recovery contact · Google: Updating our inactive account policies · FCC: SIM swap and port-out fraud rules
Related reads: Lock Your Inbox: Email 2FA, Passkeys and App Passwords · How to Change Email Providers Without Losing Your Digital Life · Not Today, Scammer